
PCI DSS Security Awareness Training for Employees
Train employees to protect payment card information.
Modern online PCI DSS security awareness training with dedicated payment card content plus practical cybersecurity instruction on phishing, social engineering, access security, information handling, responsible AI use, and incident reporting.


Security awareness is part of PCI DSS.
PCI DSS Requirement 12.6 calls for an ongoing security awareness program so personnel understand their role in protecting payment card data and the systems, devices, and processes that support it.

Train employees on the responsibilities that affect payment card security.
PCI DSS does not expect every employee to become a specialist. It does expect organizations to provide security awareness training so personnel understand the risks, warning signs, and handling practices that help protect payment card information.
- Recognize phishing and social engineering attempts
- Understand acceptable use of devices and technology
- Handle payment information through approved channels only
- Recognize suspicious vendor, terminal, or access activity
- Know how to respond and report concerns appropriately
Keep the program current.
Review the awareness program at least every 12 months and update it as threats, technologies, policies, and responsibilities change.
Train personnel regularly.
Provide security awareness training upon hire and at least once every 12 months so employees understand the practices they are expected to follow.
Address real employee risks.
Cover phishing, social engineering, and acceptable use of end-user technologies that can affect the security of the cardholder data environment.

Payment security is not only an IT responsibility.
PCI DSS Security Awareness Training is appropriate for personnel whose work can affect payment card security or expose cardholder information through handling, systems access, approvals, or support.
- Employees who accept, enter, or process payments
- Billing, finance, and customer service personnel
- Managers who approve requests, access, or vendors
- IT and support personnel working near payment systems
- Employees who may receive requests involving payment data
CFISA PCI DSS Security Awareness Training is designed to support the employee-training component of an organization’s broader PCI DSS program. PCI DSS compliance also depends on the organization’s applicable controls, policies, technologies, processes, and validation requirements.
Teach employees where payment data gets exposed.
CFISA turns PCI DSS concepts into real employee decisions, from handling payment information correctly to recognizing suspicious requests, vendor activity, and payment-terminal warning signs.

Employees practice the decision before they face it at work.
In the PCI-specific lesson, the learner works through a realistic situation involving an urgent request for customer payment card information and must choose the safe response.
The course reinforces that urgency does not override approved handling procedures. Employees learn to avoid the wrong channel, verify the request, preserve the evidence, and report suspicious activity.
The wrong data.
Employees learn what payment information requires protection, what should never be unnecessarily exposed, and why data minimization matters.
The wrong channel.
Employees learn not to send, store, or share cardholder information through unapproved methods simply because a request feels urgent or legitimate.
The wrong access.
Employees learn to notice suspicious vendor behavior, unusual access, device tampering, and unsafe activity around payment systems and terminals.
See exactly what employees learn.
Both courses include dedicated PCI DSS payment card security instruction. Choose Essentials for focused employee awareness training or Complete for broader cybersecurity coverage.
PCI DSS Security Awareness Training – Essentials 14 lessons · Approx. 1 hour 22 minutes
- 01 Why Security Awareness Matters to You 5:19
- 02 Threats, Threat Actors, and Their Motivations 4:01
- 03 Classifying and Locating the Information You Protect 3:30
- 04 PCI DSS: Protecting Payment Card Information 10:03
- 05 Social Engineering: Manipulation Tactics and Red Flags 3:48
- 06 Phishing, Spear Phishing, and Quishing Attacks 11:40
- 07 Business Email Compromise: Recognizing and Stopping BEC 5:13
- 08 Passwords, Passphrases, and Multi-Factor Authentication 4:32
- 09 Protecting Your Workspace and Securing Physical Access 3:15
- 10 Secure Storage, Disposal, Sanitization, and Record Retention 4:57
- 11 Remote Work, Travel Security, and Public Wi-Fi Risk 3:45
- 12 Safe Internet Use, Acceptable Use Policy, and Generative AI 5:42
- 13 Responsible AI Awareness: Using AI Safely, Ethically, and Within Policy 11:07
- 14 Stop, Verify, Preserve, Report: Your Security Response Model 4:58
PCI DSS Security Awareness Training – Complete 19 lessons · Approx. 1 hour 48 minutes
- 01 Why Security Awareness Matters to You 5:19
- 02 Threats, Threat Actors, and Their Motivations 4:01
- 03 Foreign Adversary Awareness: Influence Operations and Suspicious Contacts 9:27
- 04 How Attackers Exploit Predictable Employee Behavior 3:57
- 05 Classifying and Locating the Information You Protect 3:30
- 06 PCI DSS: Protecting Payment Card Information 10:03
- 07 Social Engineering: Manipulation Tactics and Red Flags 3:48
- 08 Phishing, Spear Phishing, and Quishing Attacks 11:40
- 09 Business Email Compromise: Recognizing and Stopping BEC 5:13
- 10 Passwords, Passphrases, and Multi-Factor Authentication 4:32
- 11 Protecting Your Workspace and Securing Physical Access 3:15
- 12 Secure Storage, Disposal, Sanitization, and Record Retention 4:57
- 13 Remote Work, Travel Security, and Public Wi-Fi Risk 3:45
- 14 Mobile Devices, IoT, and Device Management Best Practices 3:41
- 15 Safe Internet Use, Acceptable Use Policy, and Generative AI 5:42
- 16 Responsible AI Awareness: Using AI Safely, Ethically, and Within Policy 11:07
- 17 Social Media Security and Oversharing Risks 5:36
- 18 Identity Theft: Recognizing and Preventing Workplace Exposure 2:33
- 19 Stop, Verify, Preserve, Report: Your Security Response Model 4:58
Designed to support more learners.
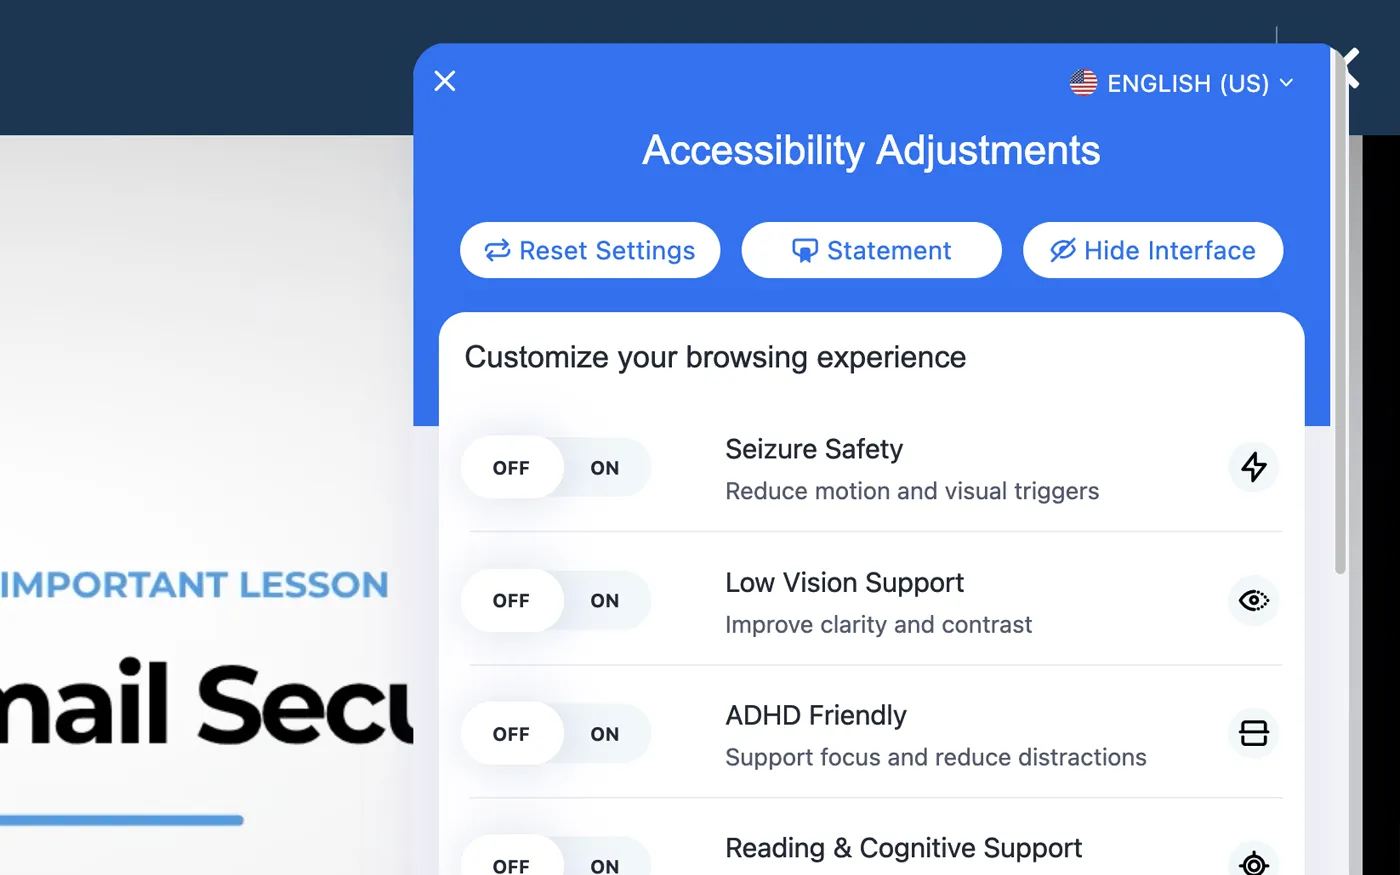
CFISA training is delivered through LightSpeed VT, which documents support for WCAG 2.0 accessibility practices, screen readers including JAWS, and closed-captioned video.
Employees can be training within minutes.
CFISA-hosted eLearning is designed to get a workforce from purchase to assigned training without a long implementation project or complicated provisioning process.
Create your company account.
Complete the company setup and access the CFISA eLearning course library.
Add employees and choose their training.
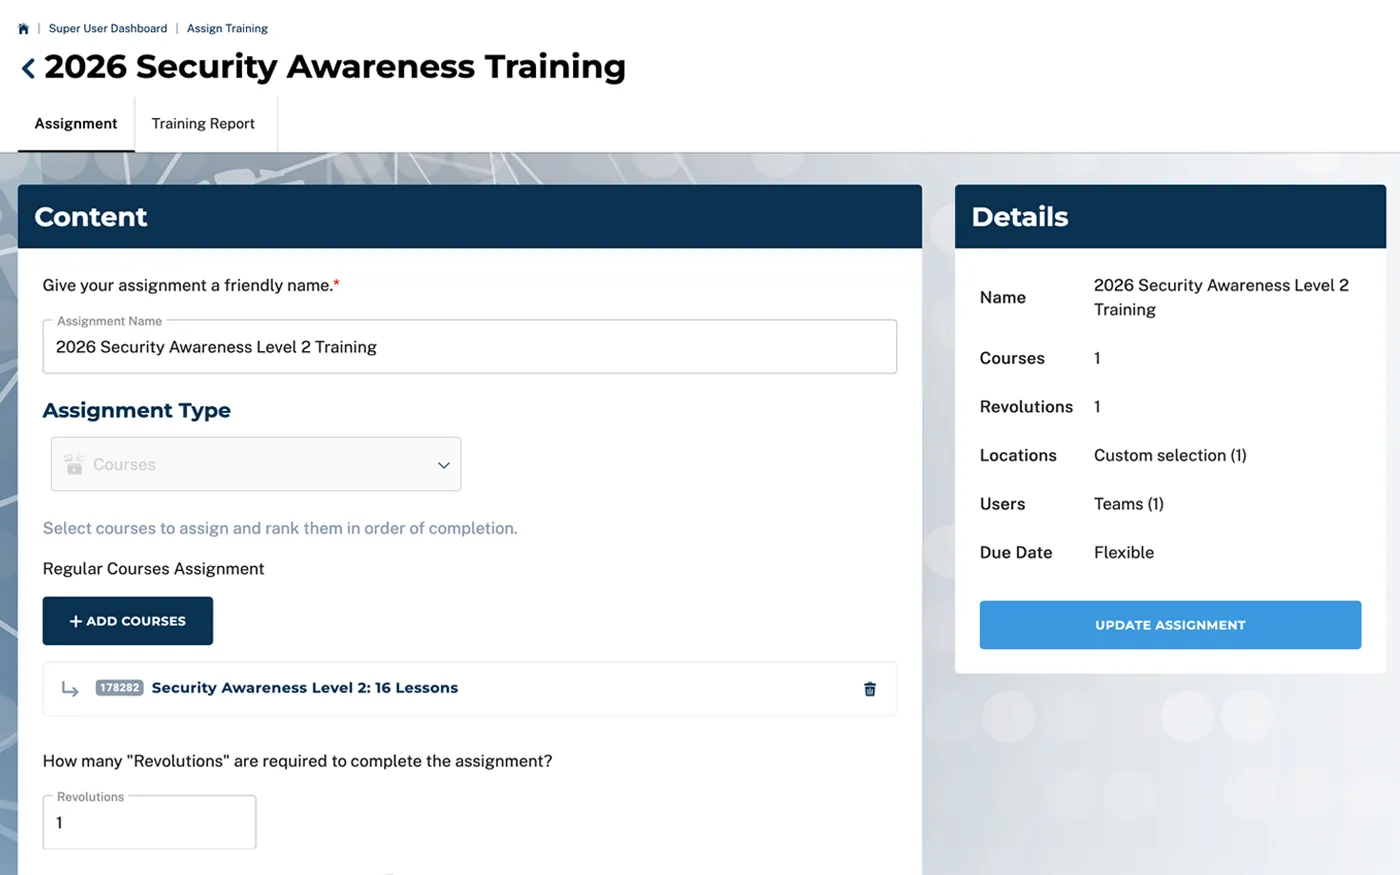
Assign employees individually or in bulk, then choose the appropriate PCI DSS course or other CFISA training based on each employee’s role.
Set the due date and go live.
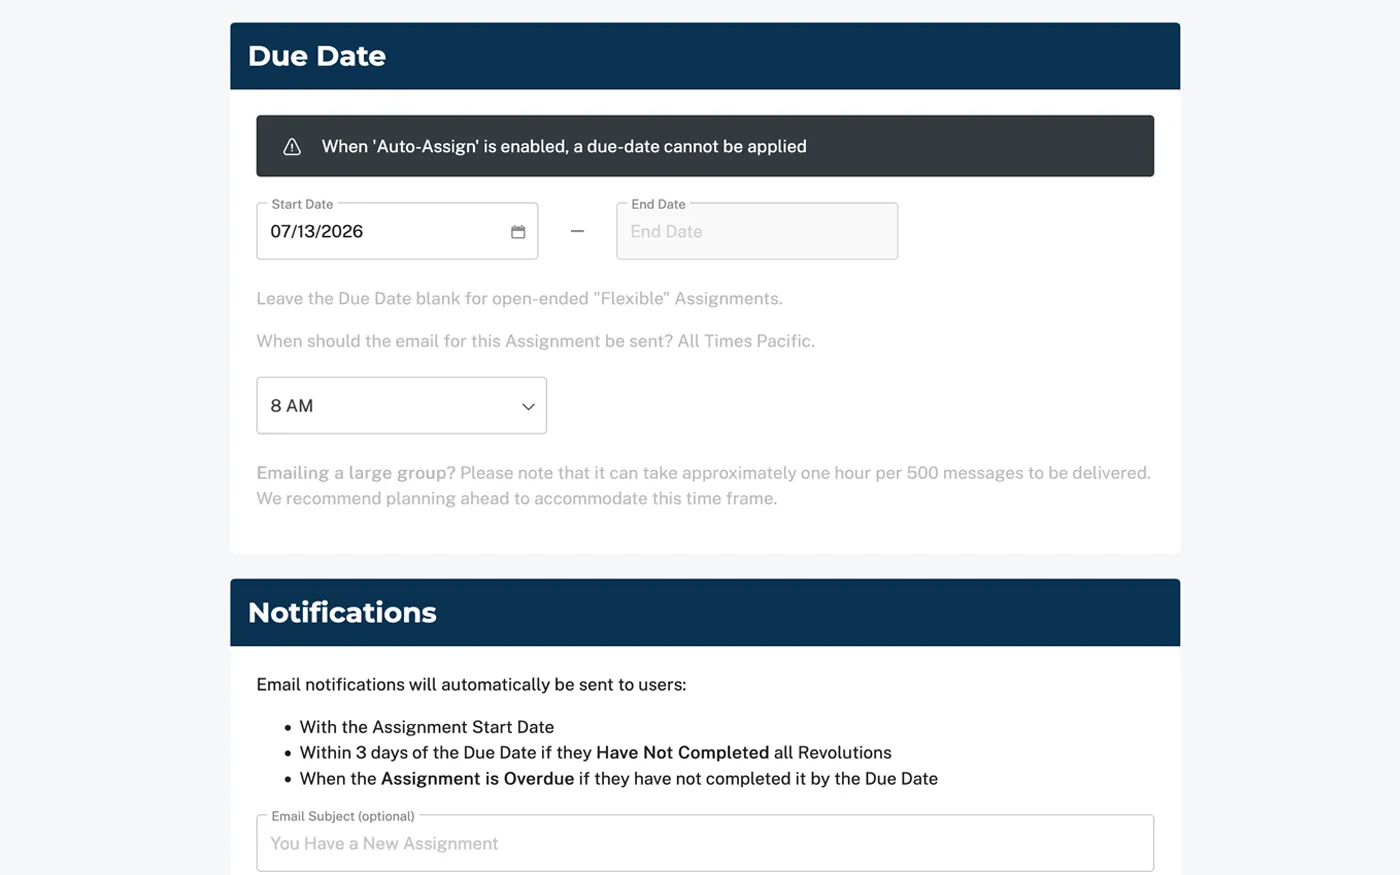
Configure the assignment details, activate the training, and let employee notifications begin.
Add 1 employee or 100. Set it once. Keep it running.
The platform is built so organizations can manage a small team or a larger workforce without turning annual training into a manual process.
Add a single employee at any time or load many users at once.
Use an Excel file to import users and create a custom email message.
New users can be added automatically to an existing assignment.
Assign PCI to card handlers, HIPAA to healthcare teams, and Security Awareness to broader staff groups.
Reduce manager logins by sending progress updates automatically.
Give more than one manager visibility into the same training program.
Track completion.
Keep the records your organization needs.
Managers can monitor employee progress and completion while each successful learner receives a dated Certificate of Completion.
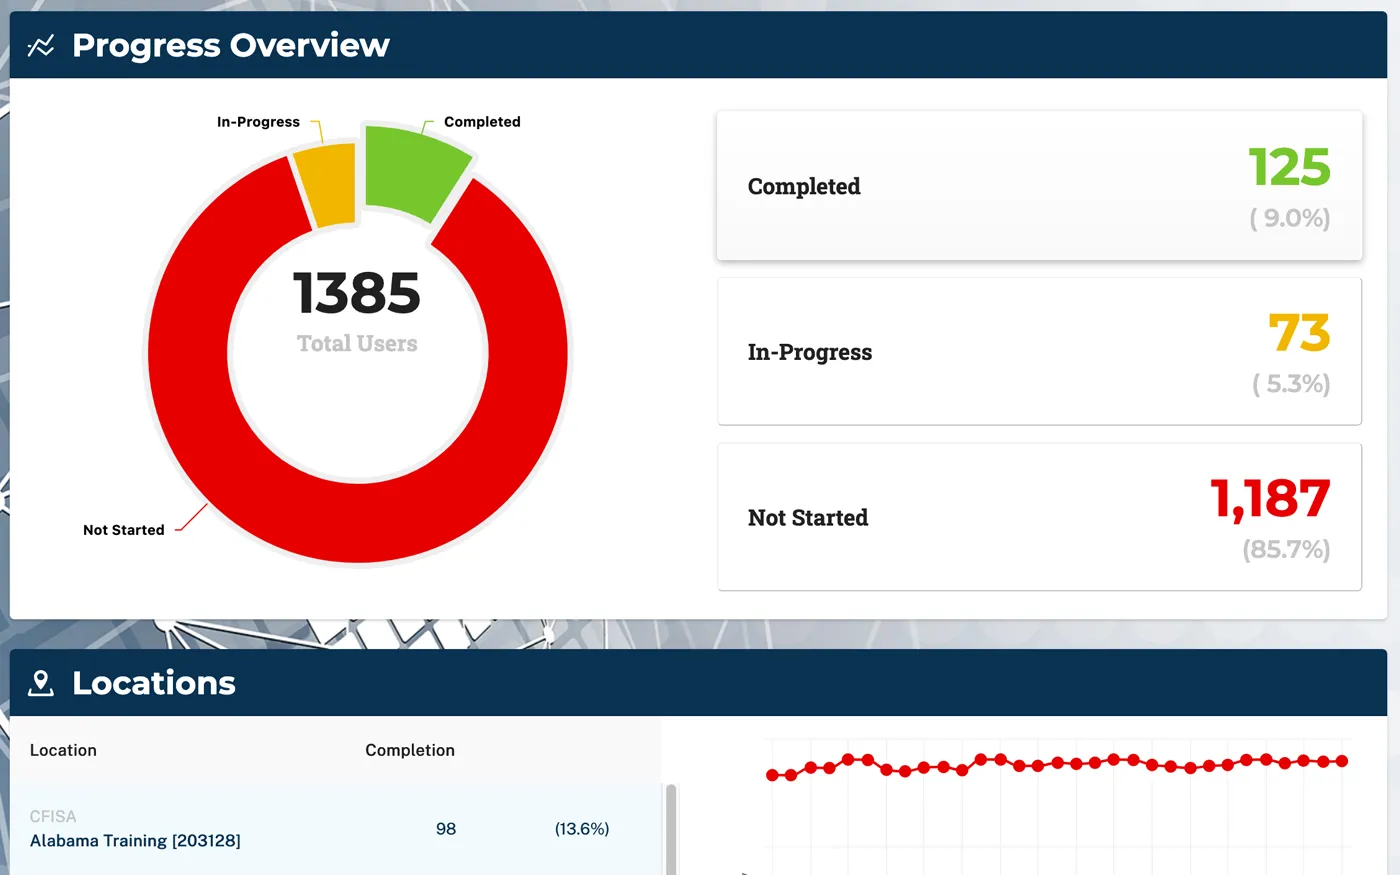
Know who has completed training and who still needs it.
Review progress without relying on manual spreadsheets or self-reported status.
- Progress overview by assignment or group
- Individual learner completion status
- Downloadable PDF and CSV reports
- Multi-location usage reporting
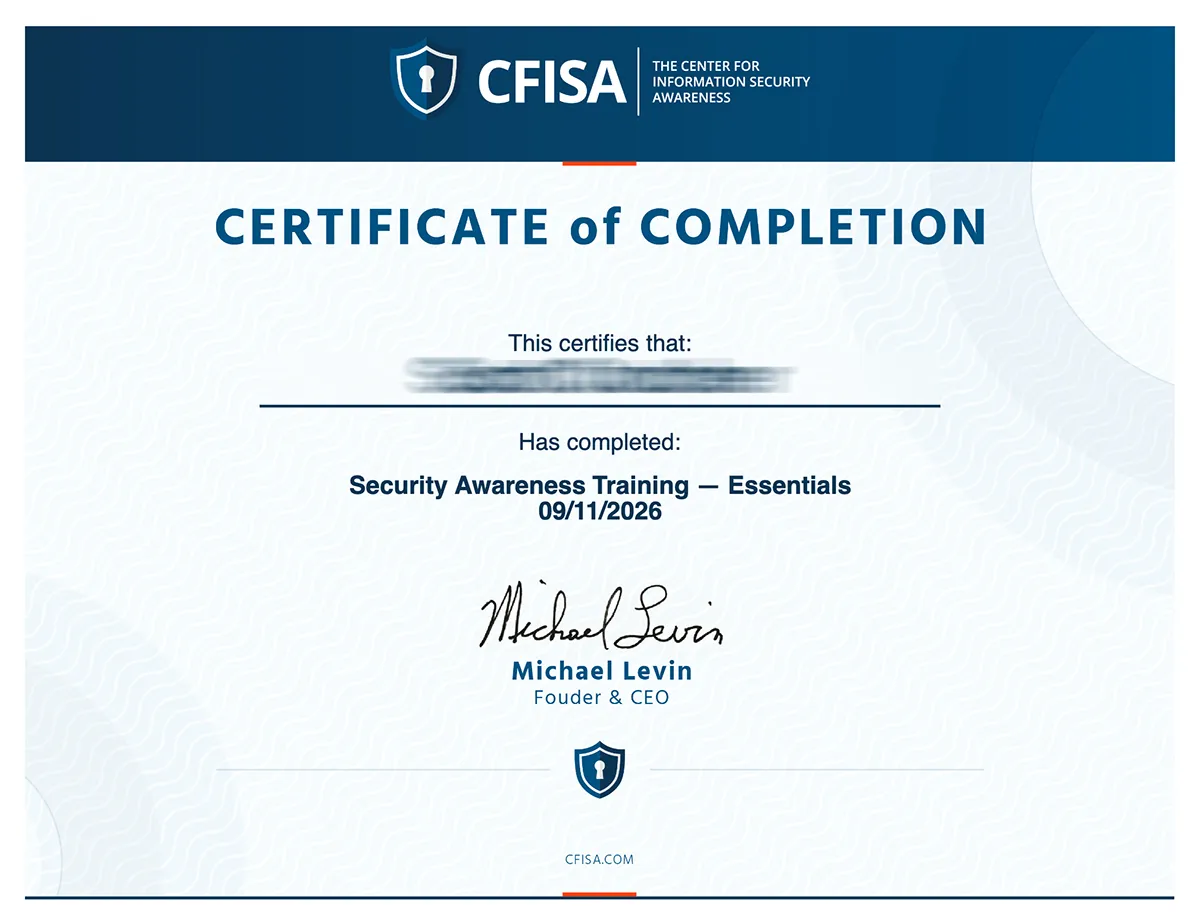
Useful for audits, training records, and annual documentation.
A dated Certificate of Completion gives the organization and employee an individual training record.
- Supports company and government audit documentation
- Provides individual proof of course completion
- Can be retained with HR or training records
- Helps document annual training and renewal cycles
Certificates document completion of CFISA training. They do not independently establish compliance with every regulatory obligation.

Cybercrime experience behind every CFISA course.
Michael Levin spent decades investigating cybercrime, protecting information systems, and leading cybersecurity programs before turning that experience into practical employee training.
Pay for employees who train. Not unused seats.
CFISA gives organizations a straightforward way to deploy PCI DSS security awareness training without purchasing annual licenses for employees who may never use them.
Plus a $4.95 one-time company account setup fee. You pay for employees who actually train during the month. Employees sitting on your roster who do not train that month are not billed.
- PCI DSS Security Awareness Training – Essentials
- PCI DSS Security Awareness Training – Complete
- Access to CFISA’s available eLearning course library
- Interactive assessments
- Certificates of Completion
- Manager progress and completion reporting
- One company account
- Usage-based billing
Start with the employees who need PCI DSS training now.
Add employees as needed and assign the training appropriate for each role. You are not purchasing a fixed annual block of unused licenses.
Start PCI DSS TrainingStraight answers about PCI DSS Security Awareness Training.
Understand who should train, what PCI DSS expects from a security awareness program, which CFISA course to assign, and how employee completion is documented.
Employees can be training in minutes.
Start online with CFISA eLearning. Your account includes PCI DSS Security Awareness Training – Essentials and Complete, along with access to CFISA’s available eLearning course library.